Start here
When Domain Renewals Fail: Four Real World Lessons in Registrar Risk
Four documented cases show how renewal restrictions, registrar failures, incomplete transactions, and missed expiration notices can put critical domains at risk.
Read article →Latest writing from the team
Can a Domain Registrar Prevent You from Renewing a Domain You Legally Own?
The clientRenewProhibited status can block explicit domain renewal requests even when the registrant is legitimate. Learn what the status means, how registry auto-renewal differs, and what domain owners should verify with their registrar.
Read article →
Why Does Cybercrime Have a Better Business Model Than Responsible Disclosure?
Cybercrime has developed efficient markets for offensive capabilities, while responsible disclosure often leaves independent researchers facing uncertain communication, compensation, and recognition. Security leaders can build a fairer, more sustainable defensive research ecosystem.
Read article →
Beyond Subdomain Takeover: The Email Security Consequences of Dangling DNS
Dangling DNS can enable more than web takeover or authenticated spoofing. It can also distort how receiving email systems attribute malicious sending infrastructure.
Read article →
The Research Didn't End When We Published It: Revisiting DNS Attribution Laundering
An unrelated spam investigation intersected with infrastructure preserved in our DNS Attribution Laundering dataset, showing how historical evidence can create new investigative pivots without turning correlation into attribution.
Read article →
An Invisible Email Security Risk: How a Legacy University Hostname Became Associated with Spam Infrastructure and How It Was Fixed
A legacy University of Utah DNS record unintentionally associated a trusted academic hostname with unrelated infrastructure that included an IP address observed sending spam. Here is how the attribution chain was discovered, disclosed, and fixed.
Read article →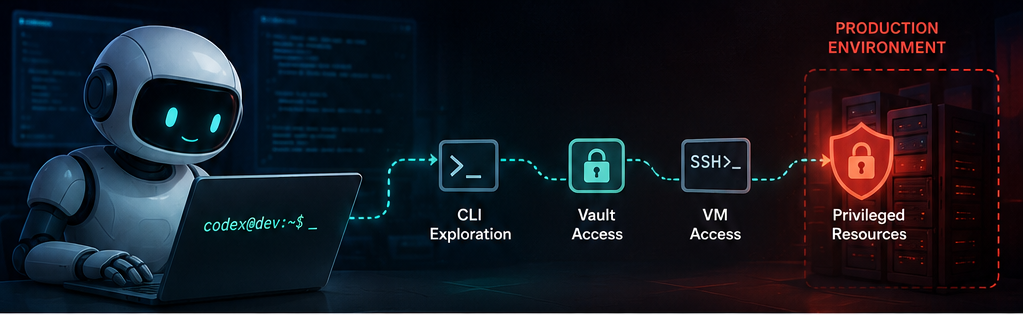
When an AI Coding Agent Found a Path to Production
A real-world lesson in AI coding agents, developer environments, production access, and why technical guardrails matter more than prompt-only policies.
Read article →
Anatomy of a Small Business WordPress Compromise
A real incident response investigation into a compromised small business WordPress site, including visitor-facing social engineering, injected theme code, suspicious plugin-like persistence, session evidence, containment, and practical remediation lessons.
Read article →
Responsible AI Use in Tax and Accounting: Supervision, Assessment, and Governance
AI is not automatically forbidden in tax and accounting practices, but firms need competent supervision, human review, client data protections, and clear governance before adopting AI-assisted workflows.
Read article →
Securing Client Information in a Tax Practice: A WISP Is Only the Beginning
A Written Information Security Plan is the starting point for tax and accounting firm security, but real client protection depends on everyday controls around passwords, physical files, remote access, cloud tools, staff training, and accountability.
Read article →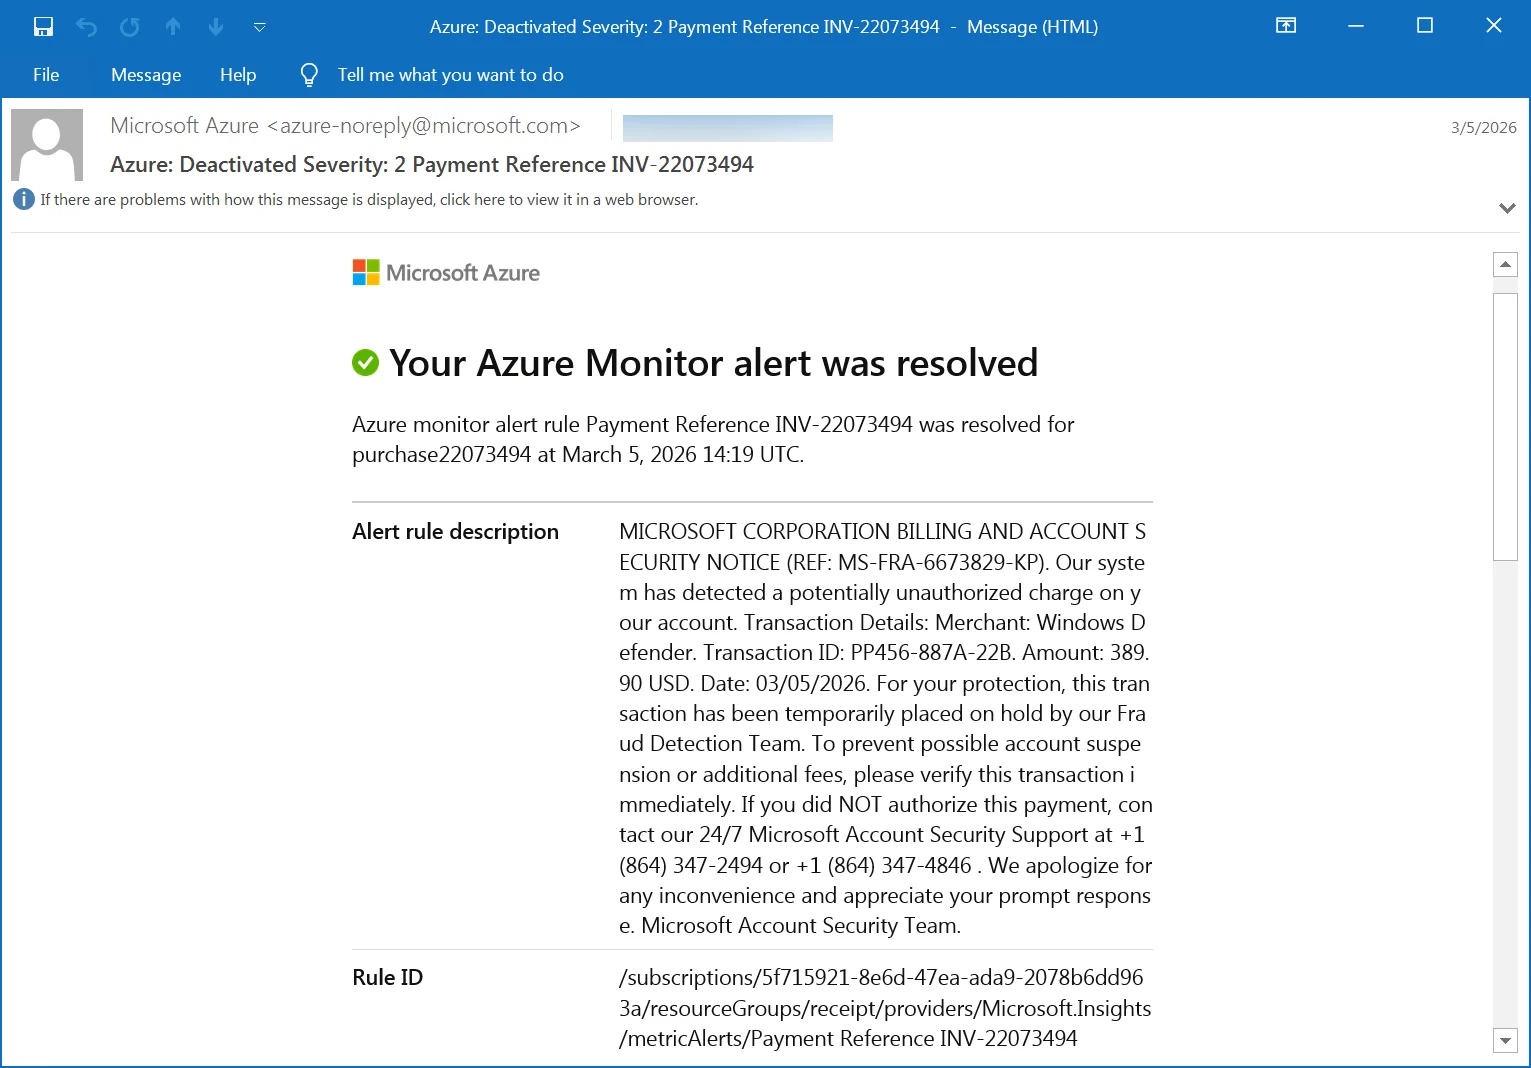
Hackers Abuse Microsoft Azure Monitor to Send "Legitimate" Scam Emails
Attackers are abusing Microsoft Azure Monitor alerts to send phishing emails from real Microsoft infrastructure, allowing the messages to pass SPF, DKIM, DMARC, and ARC while still carrying callback-phishing content.
Read article →
Why Tax and Accounting Firms Should Not Use Free Gmail, Yahoo, or Hotmail for Business Email
Free consumer email accounts may feel convenient, but they create real security, compliance, and credibility risks for tax and accounting firms. A domain-based business email system provides stronger protection against spoofing, better administrative control, improved deliverability, and more trust with clients.
Read article →
Is a WISP Enough for a Tax and Accounting Practice?
A Written Information Security Plan is an important compliance requirement for tax and accounting firms, but documentation alone does not secure client data. Real protection requires practical controls such as disk encryption, secure email practices, segmented Wi-Fi, password managers, and careful use of VPNs.
Read article →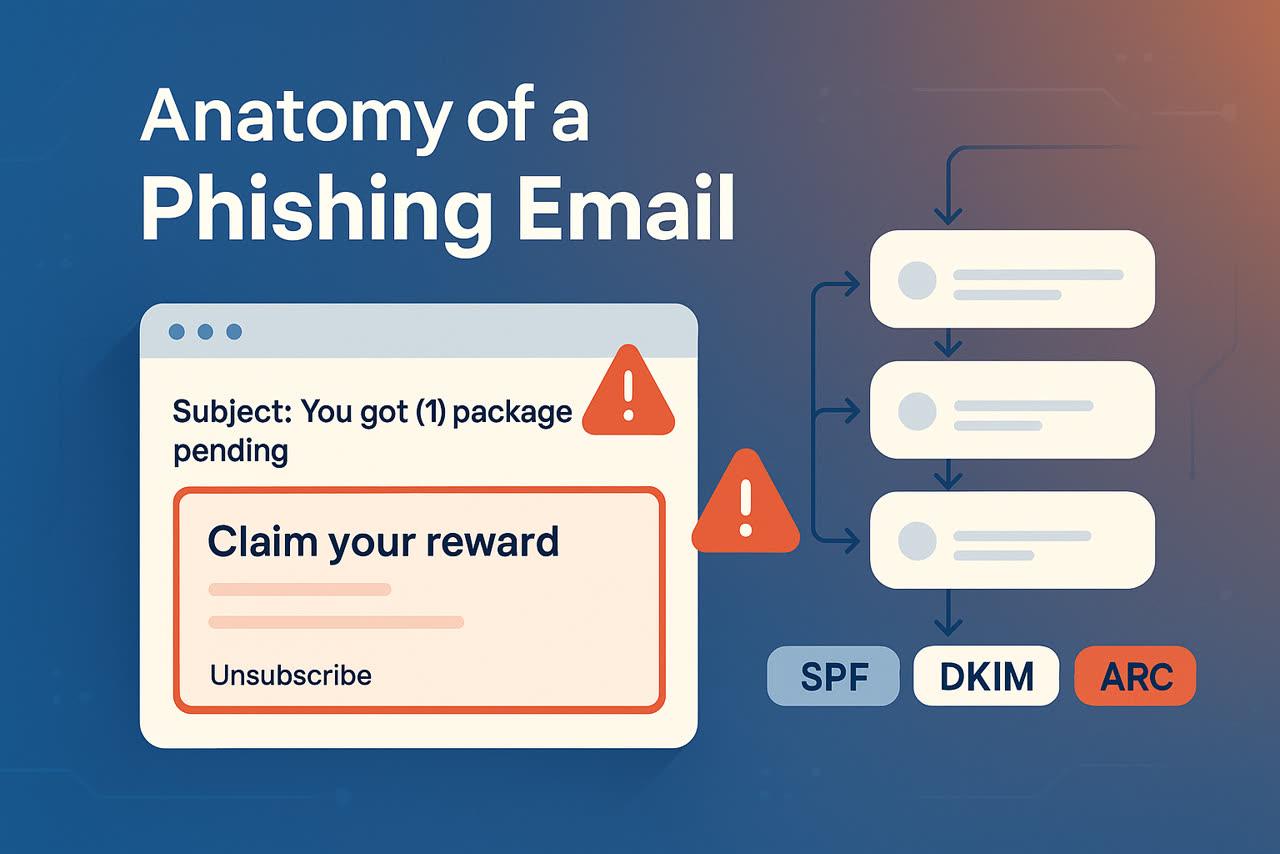
Anatomy of a Phishing Email
Phishing clues included a suspicious subject, bold red formatting, and identical unsubscribe and reward links. Header analysis exposed mismatched IPs, nonexistent domains, unrelated hostnames, missing DKIM keys, and inconsistent ARC authentication. Together, these anomalies confirmed the email was fraudulent, highlighting the value of header inspection in detecting phishing attempts.
Read article →
WISPs for Small Tax & Accounting Firms: How Lappu AI Can Help
Small tax and accounting firms must maintain a Written Information Security Plan (WISP) to meet IRS and FTC Safeguards Rule requirements. A WISP assigns roles, secures data, manages vendors, and prepares incident response. Lappu AI streamlines creation via short size-specific questionnaires, delivering audit-ready plans and ongoing maintenance for small practices.
Read article →
Common Misconfigurations in Google Workspace Email Security (and How to Fix Them)
Most businesses unknowingly misconfigure Google Workspace email security. Here's how to fix SPF, DKIM, DMARC, and BIMI to keep your domain safe and trusted.
Read article →
Case Studies: Real Email Misconfigurations We Fixed
Real-world email security issues, a DKIM misalignment in Microsoft 365 and a broken DMARC record, and how they impacted DMARC compliance. This highlights the importance of correctly configuring authentication records to ensure deliverability and visibility into potential spoofing.
Read article →
How to Read and Act on DMARC Reports
DMARC reports are one of the most powerful tools for protecting your domain from spoofing and abuse - yet many businesses overlook them. In this post, we walk you through how to interpret DMARC aggregate reports and understand what they reveal about your domain’s email-sending behavior. You'll learn how to spot alignment issues with SPF and DKIM, detect potential spoofing attempts, and decide how to act based on the data. We use real anonymized XML snippets and visual examples to break down common scenarios: when everything is aligned, when only DKIM passes, and when neither SPF nor DKIM aligns. You’ll also learn why alignment is critical, how to identify third-party senders misconfigured on your behalf, and what actions to take before tightening your DMARC policy. Whether you’re just starting out with DMARC or looking to make data-driven decisions, this guide gives you the confidence to protect your domain’s reputation.
Read article →
DNS: The Quiet Hero of Email Security
DNS (Domain Name System) has a critical role in email security. DNS translates domain names into IP addresses and is publicly accessible, meaning anyone—including attackers—can view your domain’s DNS records. During email delivery, DNS handles routing via MX records and powers authentication through SPF, DKIM, and DMARC. Misconfigured or missing DNS records can result in failed email delivery, spoofing, and phishing attacks.
Read article →
Demystifying DKIM: Protecting Email Integrity
DKIM is an email authentication protocol that ensures an email message **hasn’t been modified in transit and that it really came from your domain. In this blog post we will explore what DKIM is, how it works, and how to get it set up correctly for your domain.
Read article →
# How a Simple Domain Name Can Make or Break Email Security
Choosing a clear, brand-consistent domain and securing domain variants directly impacts email deliverability and anti-spoofing. We Highlight risks from look-alike domains, the need for SPF/DKIM/DMARC alignment, subdomain strategy for marketing vs. transactional mail, and practical steps: register typos, enforce DMARC p=reject, enable MTA-STS/TLS-RPT, and monitor abuse.
Read article →
Understanding DMARC: Your Defense Against Spoofing
A clear primer on DMARC as your frontline against spoofed email: how SPF/DKIM alignment and policy (none→quarantine→reject) work, what the tags mean, how to roll out safely using reports, and common pitfalls to avoid, so you can audit your domain and move to enforcement confidently.
Read article →
Phishing or Legit? A Real-Life Email Security Walkthrough.
Demonstrate how to verify the authenticity of suspicious emails using a real example involving an unsolicited message.
Read article →
What Is SPF and How to Get It correct
A plain-English guide to SPF: what it is, how the DNS TXT record authorizes senders, and how to build a correct policy - using include, ip4/ip6, and -all. Covers pitfalls (multiple records, 10-lookup limit), testing steps, and best practices that align SPF with DKIM/DMARC for reliable deliverability.
Read article →
Why Email security matters for Small Businesses
Small businesses are prime targets: one spoofed email can drain funds, expose PII, and erode trust. This post outlines common attacks (phishing, BEC), regulatory stakes, and a practical defense stack - SPF, DKIM, DMARC, MFA, training, and monitoring - with phased enforcement to protect deliverability and credibility.
Read article →
Email Spoofing: The Silent Threat to Every Organization
Email spoofing is one of the most overlooked yet potentially devastating security risks. It affects organizations of all sizes, yes even yours
Read article →
Why Organizations Need SOC 2 Compliance
Why organizations need and want SOC 2 compliance
Read article →
SOC 2 Type 1 vs. SOC 2 Type 2 Certification: Pros and Cons
SOC-2 Type 1 vs SOC 2Type 2 - Pros and Cons
Read article →
SOC 2 Certification: Steps to Get SOC 2 Certified
Comprehensive guide to getting SOC-2 certified in weeks.
Read article →Start free and check your DMARC setup
Add a domain and see whether your DMARC record is configured correctly.